Aegisify company logo
Aegisify: Cloud & WebApp Tools, Security Audit and Digital Intelligence2026-09-27T05:25:25+00:00
Cloud Digital Intelligence

More Than Cloud Security. Understand The Story Behind The Risk.

Turn AWS telemetry, identity, vulnerabilities, attack paths, drift, and evidence into actionable intelligence.

Aegisify Digital Intelligence

SaaS Cloud Command Center

Edge connected Investigations Evidence ledger Risk correlation
Telemetry → SaaS Policy / enrollment → Edge
AWS Account / Cloud EnvironmentREAD
APIs
EVENT
STREAMS
STATE
DB
AWS
CONFIG

DI IaaS Edge

Collect • Normalize • Correlate • Score

Inside AWS • Connected
Enabled AWS Services
Inventoried
18
Services with active resources
Active Regions
Mapped
3
Regions containing real resources
Critical Findings
Correlated
27
High-confidence security issues
64%
Identity Risk
Resolved
11
Risky roles, users, and entitlements
Cloud Drift
Compared
14
Added, removed, or changed resources
Critical Attack Paths
Prioritized
6
Reachable paths to high-value assets
Evidence & Events
Streaming
8,427
Normalized evidence records processed
WebApp Security Audit + Digital Intelligence

Is Your Web Application Exposed? Get Insights And Intelligence.

Find the signal. Filter the noise. Act with evidence.

Static Dynamic AGENT WAF

Aegisify Audit

Risk Command Center

Evidence correlated
Security Score
Live
69%
Measured posture Prioritized from verified findings.
WordPress Footprint
Mapped
Core Files Themes Plugins Database Settings Dependencies
Static Findings
Scanned
89
Code Findings identified
Dynamic Findings
Validated
124
Exposure checks validated
Vulnerabilities
Verified
152
Prioritized by risk
Attacks Blocked
Protected
219
Blocked attempts
Plugins & themes
Connected
16
15 Plugins - 1 Theme
Interactive threat scenario

The Rise Of AI Bot Attacks, Lockdown & Data Exfiltration

Do not wait till its too late, get Digital Intelligence today. Imagine your AWS, Azure, GCP, OCI, or Web Application are placed under lock pressure and data moving into Europe, Asia or the Middle East.

Lock + chain overlay Exfiltration to Europe DI telemetry storyline

AI Hacker Bot

Orchestrate • Encrypt • Exfiltrate

Lockdown active
LOCKED
AWS
Locked
41
Instances, services, and storage paths under the chain zone
Azure
Locked
18
Subscriptions and workloads appearing inside the hostile chain path
GCP
Locked
26
Projects and services visualized as locked into the compromise zone
OCI
Locked
12
Oracle cloud assets depicted under lock and chain pressure
Web Application
Locked
09
Application and content surfaces chained into the lock narrative
Remote Destination • Europe
Egress active
Data outbound transfer flow converging into Europe Asia.
Interactive details Click any provider card, the center lock, the world map, or one of the lower intelligence cards to update this narrative panel.
Blast Radius
Escalating
5
Platforms simultaneously chained into the event
Encryption Pressure
Detected
73
Locked workloads and chained application surfaces
AWS Azure GCP OCI WebApp
Exfiltration Channels
Streaming
11
Observed outbound paths to the highlighted remote endpoint

Public external scan • No authenticated access • Results are removed when you leave the page

Run a fast public security scan on any website. No login or Agent required. Connect agent when you want deeper code, plugin, dependency, log, API, and Commerce intelligence.

  • Any public website

  • Deep Web Application Visibility

  • Human-reviewable guidance

01 · Discover the exposure

Find the signal.

Combine public attack-surface testing with verified WordPress Agent evidence to uncover exposed routes, vulnerable software, code weaknesses, configuration drift, suspicious changes, and commerce risk.

Learn how it works
Unified WordPress Security Workflow

How Aegisify Works: From Exposure to Verified Defense & Action

External visibility, authorized internal evidence, active protection, and AI-supported action move through one connected security and audit workflow.

External Context
Aegisify Audit

Attack Surface Scanning

Aegisify Audit scans internet-reachable assets, exposed routes, public services, and WordPress attack paths to reveal what attackers can see.

  • External surface discovery
  • Reachable and exploitable exposure
  • Internet-visible risk signals
Internal Context
Authorized Agent

Agent Deep Analysis

The authorized Aegisify Agent adds internal intelligence from code, files, logs, configurations, dependencies, plugins, themes, WooCommerce flows, SAST, and DAST.

  • Verified internal evidence
  • Code, file, and dependency visibility
  • Application and commerce context
Defense Context
Shields + WAF

Protect, Detect & Block

Aegisify Shields protects WordPress core and applications while Aegisify WAF analyzes traffic, bots, APIs, and attacks to harden, detect, respond, and block.

  • Hardening and integrity controls
  • Firewall, bot, app and API protection
  • Detection, response, and blocking
Action Context
AI + Reporting

AI, Reports & Action

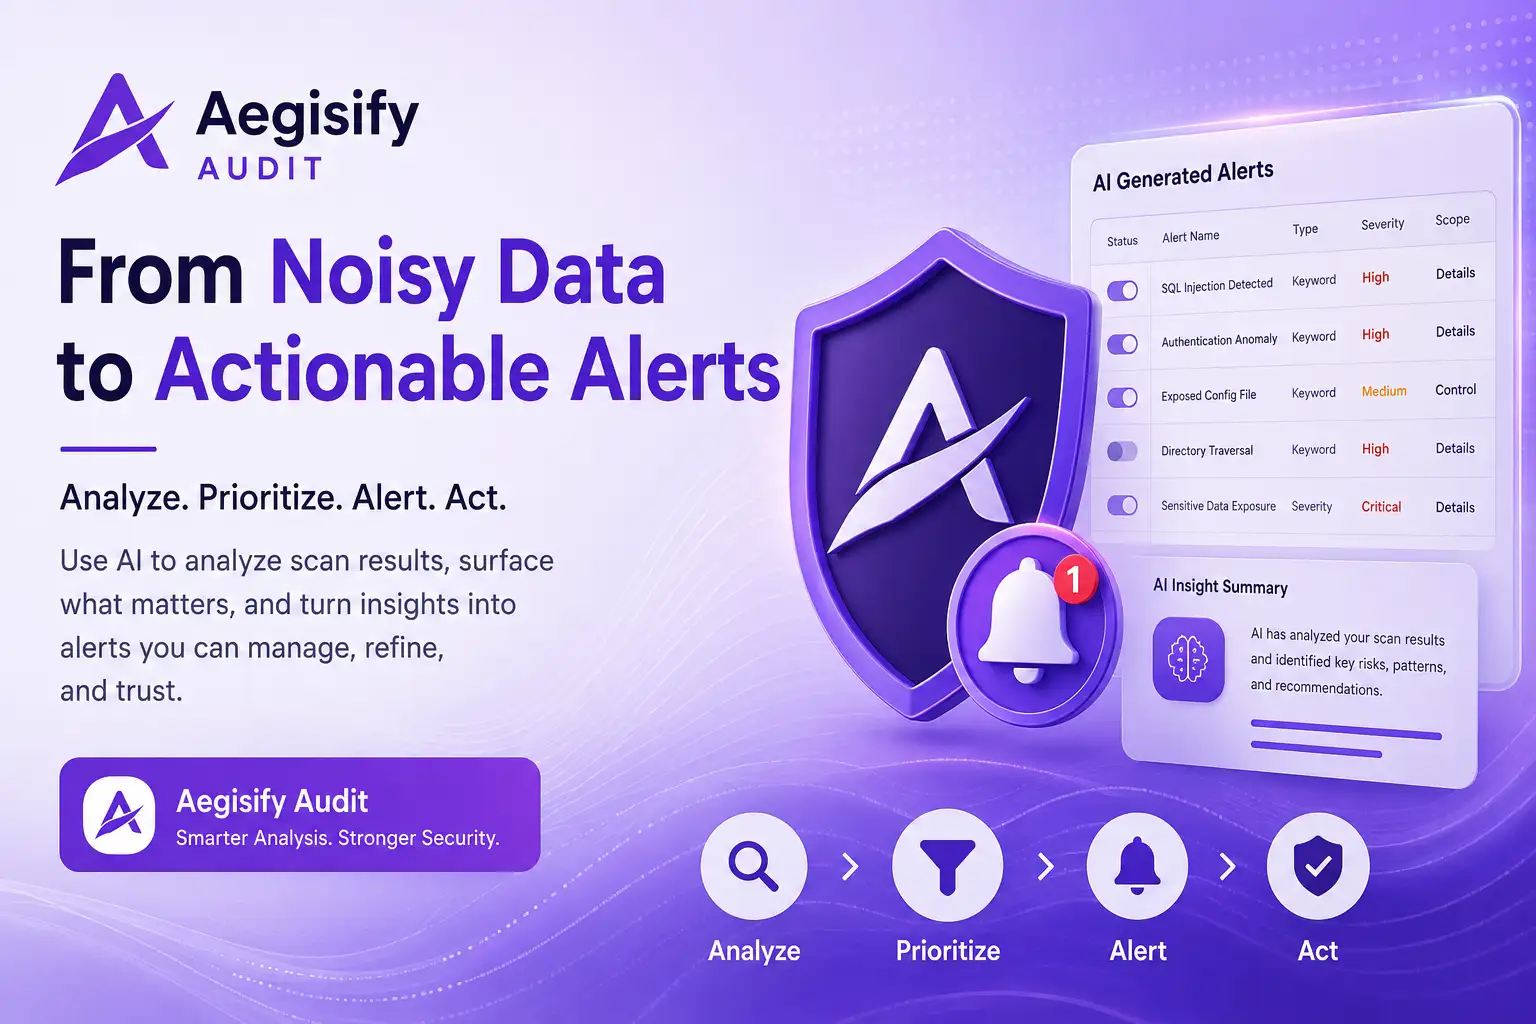
AI filters noise, prioritizes meaningful risk, recommends fixes, supports assignments, and powers weekly automated reports, notifications, and remediation tracking.

  • Prioritized findings and guidance
  • Assignments, alerts, and status
  • Evidence-backed weekly reports
Evidence remains connected from external exposure through verified remediation and reporting.
WordPress Security Audit & Risk Intelligence

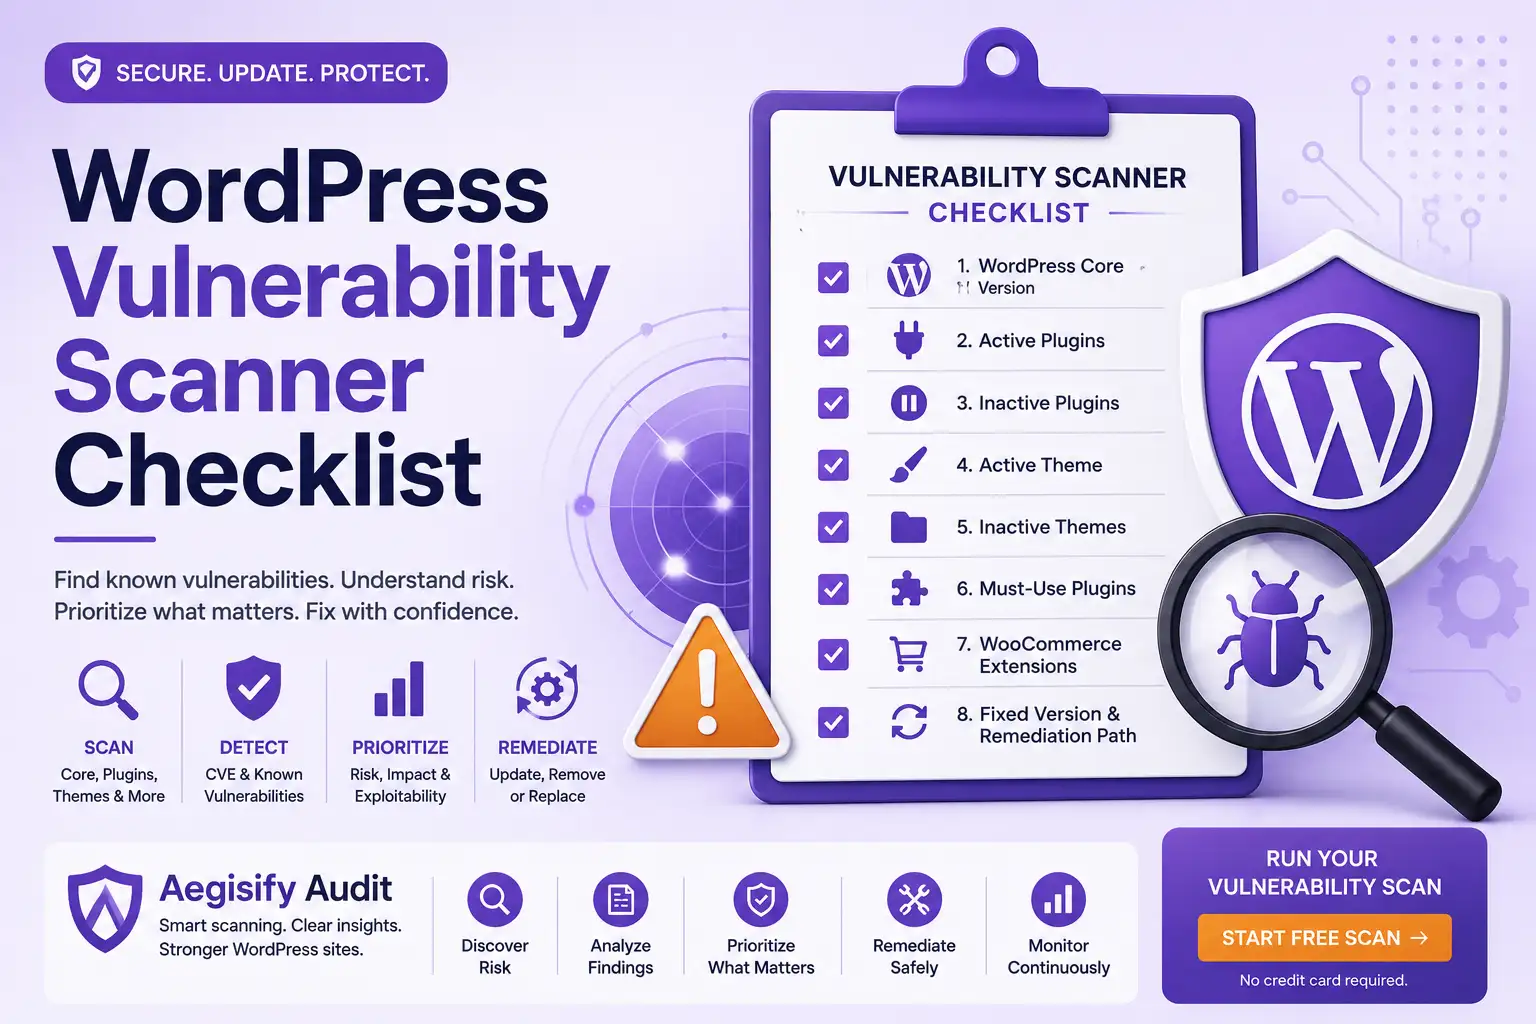
See the WordPress risk your plugin dashboard do not show.

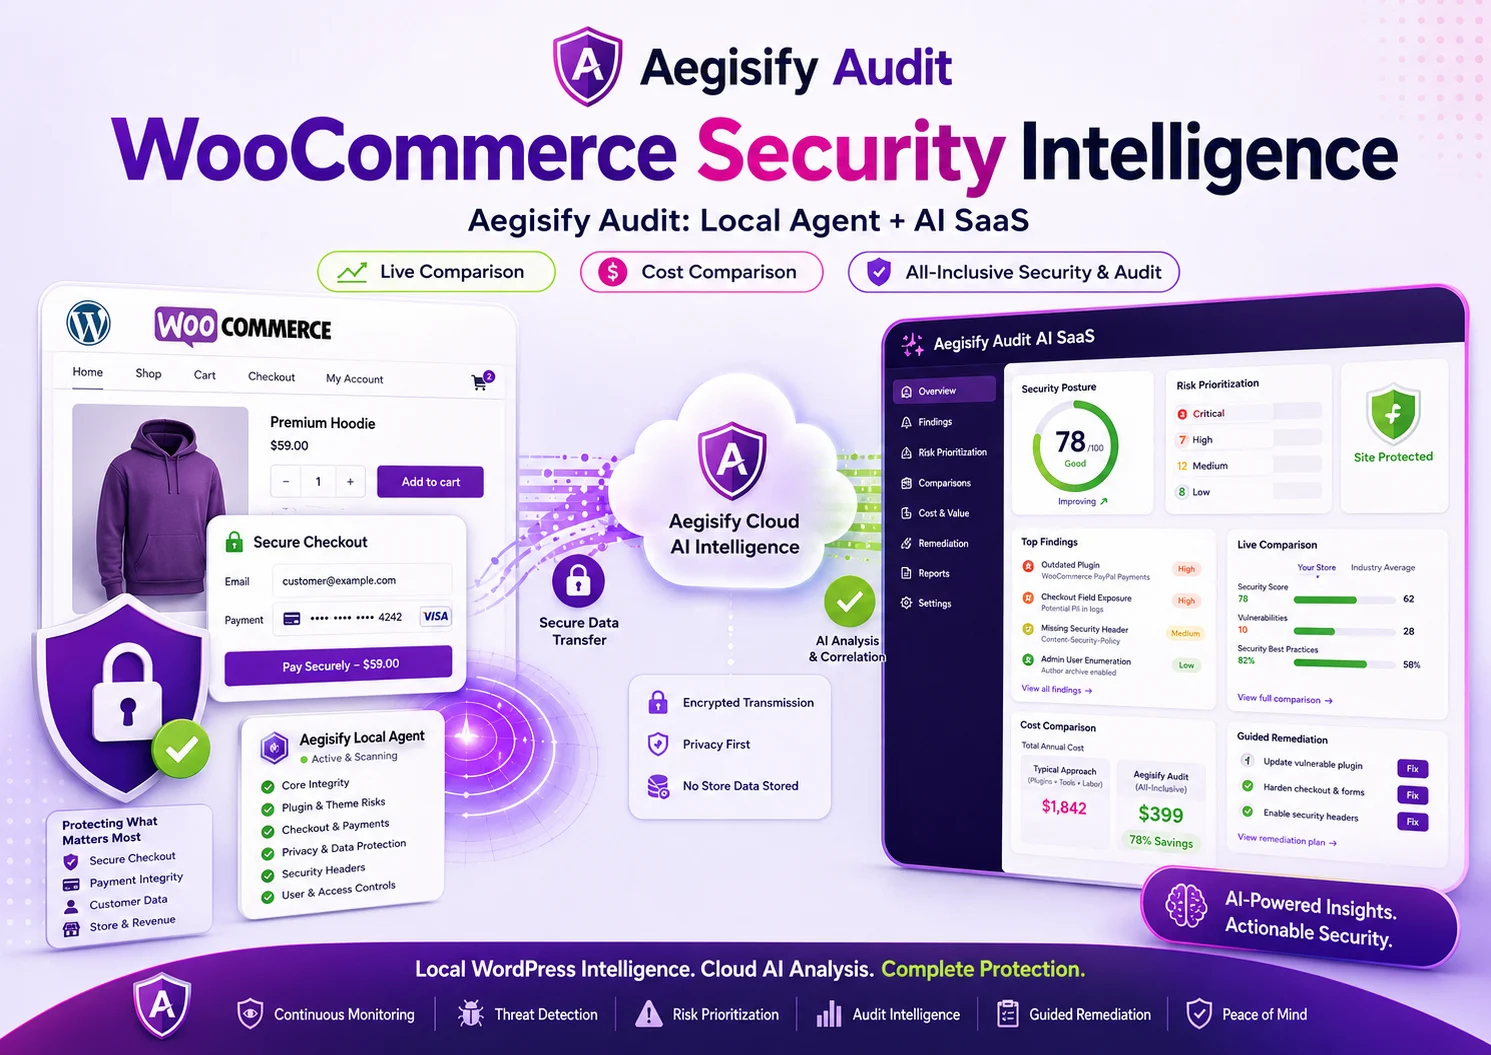
Aegisify Audit combines verified external scanning with an authorized WordPress Agent to give security leaders clear business priorities and IT teams the technical evidence needed to investigate risks, coordinate Aegisify security controls, and verify remediation across code, dependencies, web and API exposure, WooCommerce workflows, site changes, and logs.

Outside-in exposure Inside WordPress evidence Business-risk context Human-reviewable guidance
Know what runs inside the WordPress environment before it becomes a blind spot. The authorized Agent inventories core, plugins, themes, MU-plugins, Composer, npm, and PyPI packages, then connects versions, provenance, known vulnerability evidence, integrity drift, and change history. Leaders gain asset accountability; administrators get a precise investigation list. Software inventoryDependency riskChange visibility Review the evidence model
Review application logic that outside-only scanners cannot see. Agent-authorized static analysis examines WordPress code quality, PHPCS/WPCS signals, custom PHP, JavaScript and supported Python rules, secrets, malware indicators, nonces, capabilities, and REST/AJAX authorization. Prioritize code paths that can affect sensitive data, privileges, transactions, or uptime. Static analysisAuthorization reviewCode evidence Explore application security
Test the public WordPress application as an attacker-facing surface—not only as a plugin inventory. Quick DAST, Enterprise DAST: App & Commerce, Deep Auth DAST, and API DAST review routes, headers, cookies, forms, REST, OpenAPI, GraphQL, sessions, and authorization boundaries with evidence tied to each finding. Public exposureAPI discoveryAuth boundaries See the scan workflow
Follow the business flow from cart to order instead of treating WooCommerce as another plugin. Review Store API, checkout blocks, payment paths, webhooks, HPOS, Action Scheduler, order ownership, privacy, templates, extensions, and abuse signals that can become revenue loss, fraud exposure, operational failure, or damaged customer trust. Revenue pathsOrder integrityCommerce operations Review commerce coverage
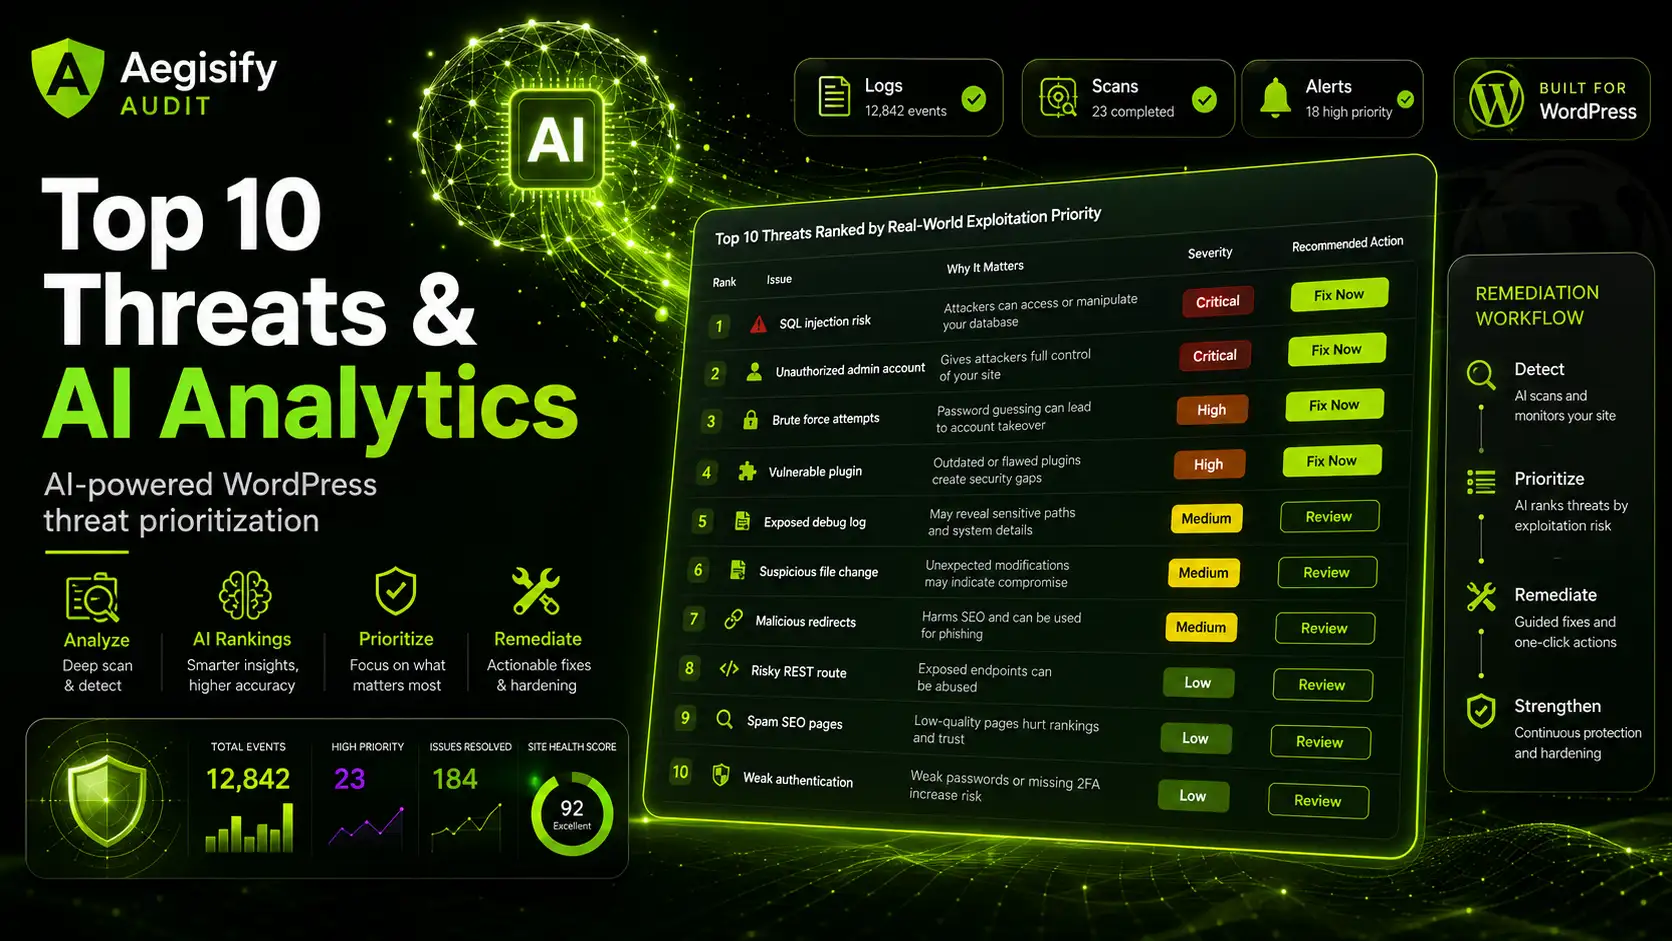
Give executives the decision view and administrators the technical proof. Correlate findings with the affected asset, evidence, severity, confidence, threat intelligence, scan deltas, remediation status, and verification notes. Use human-reviewable AI triage and CSV, PDF, or XML reports to decide what to fund, fix, and verify first. Prioritized riskHuman reviewDefensible reporting See facts and proof
Asset Intelligence / Verified DomainWordPress & Dependency Inventory
Inventory Connected
Evidence sourceAgentAuthorized local collection
Software layers7Core through dependencies
Risk signalsLinkedVulnerability + provenance
Site changeTrackedAdded, removed, changed
WordPress Software Map
Inventory, versions, provenance, and change evidence
Inside View
WPCore + runtime
PL
PluginsActive + MU
TH
ThemesActive + parent
CP
ComposerPHP packages
JS
npmJS packages
PY
PyPIPython packages
Dependency Risk Intelligence
Evidence attached to the affected component
Correlated
CV
Known vulnerability matchingCVE, OSV and WordPress-focused evidence
Mapped
KE
Exploit and likelihood contextKEV and EPSS signals where available
Context
DR
Inventory driftAdded, removed, or version-changed software
Tracked
IN
Integrity and support signalsMismatch, inactive, abandoned, or unsupported risk
Review
Leadership answer: What software exists, what changed, and which components deserve action?Replace assumptions and screenshots with domain-bound inventory and evidence that technical teams can investigate.
Asset accountability
1 / 5

All it takes is 30 minutes, you will love us!​​​​​​

14 days Free Trial. Cancel anytime with no pressure, no spam emails or phone calls.